Full ISO/IEC 27001 Pack: editable documentation templates for ISO 27001:2022 readiness
Stop calling another meeting. Hand them the documents.
ISO/IEC 27001:2022 readiness pack for the Chief Information Security Officer (CISO): 25 editable files in 16 modules.
Readiness documents, not a certification. Word, Excel and PDF.
What are ISO 27001 readiness documents?
ISO 27001 readiness documents are a set of guides and templates that walk your organization through a mock audit, your internal audit, and preparing for your Stage 1 audit. The pack gives you editable files your team fills in, so the documents an auditor asks for already exist and have owners.
Know where you stand
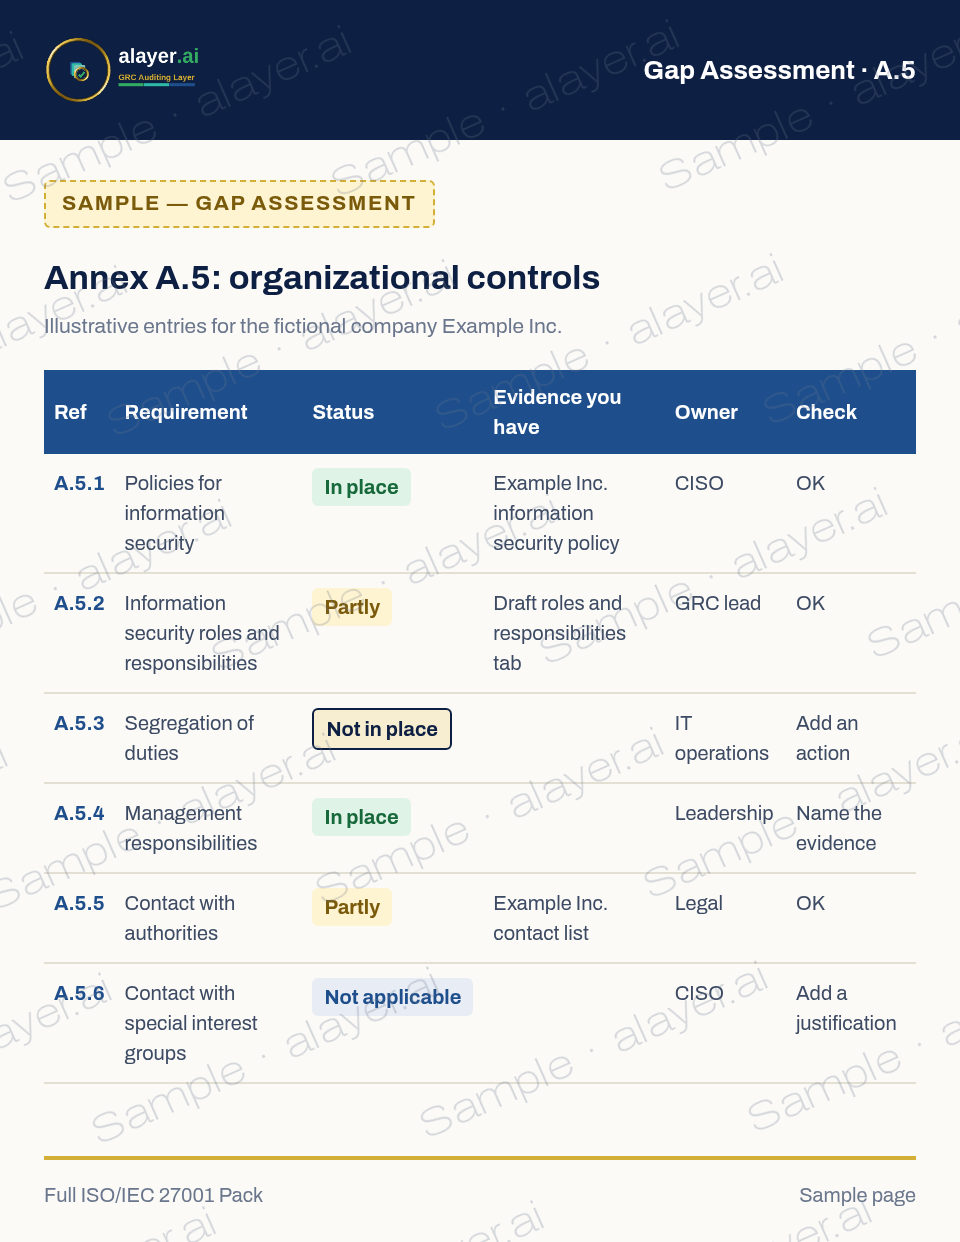
The Gap Assessment works like a mock audit: it shows where you stand.
Build the evidence
Area-of-work files and evidence guides.
Run your internal audit and walk into Stage 1 prepared
The CISO Meeting Kit and a documented Statement of Applicability (SoA) worksheet your team completes.
Reviewed, not generated
Generic artificial intelligence (AI) can draft a policy. It can’t hand your auditor a consistent, reviewed evidence pack.
Who it’s for
- CISO running ISO/IEC 27001:2022 readiness and handing each file to its owner
- Governance, risk and compliance (GRC) lead using the Gap Assessment, registers and risk files
- Identity and cloud engineers using the evidence guides for Microsoft Entra ID and Microsoft Azure
- Information technology (IT) operations covering assets, vulnerabilities, configuration, networks and endpoints
See a sample page
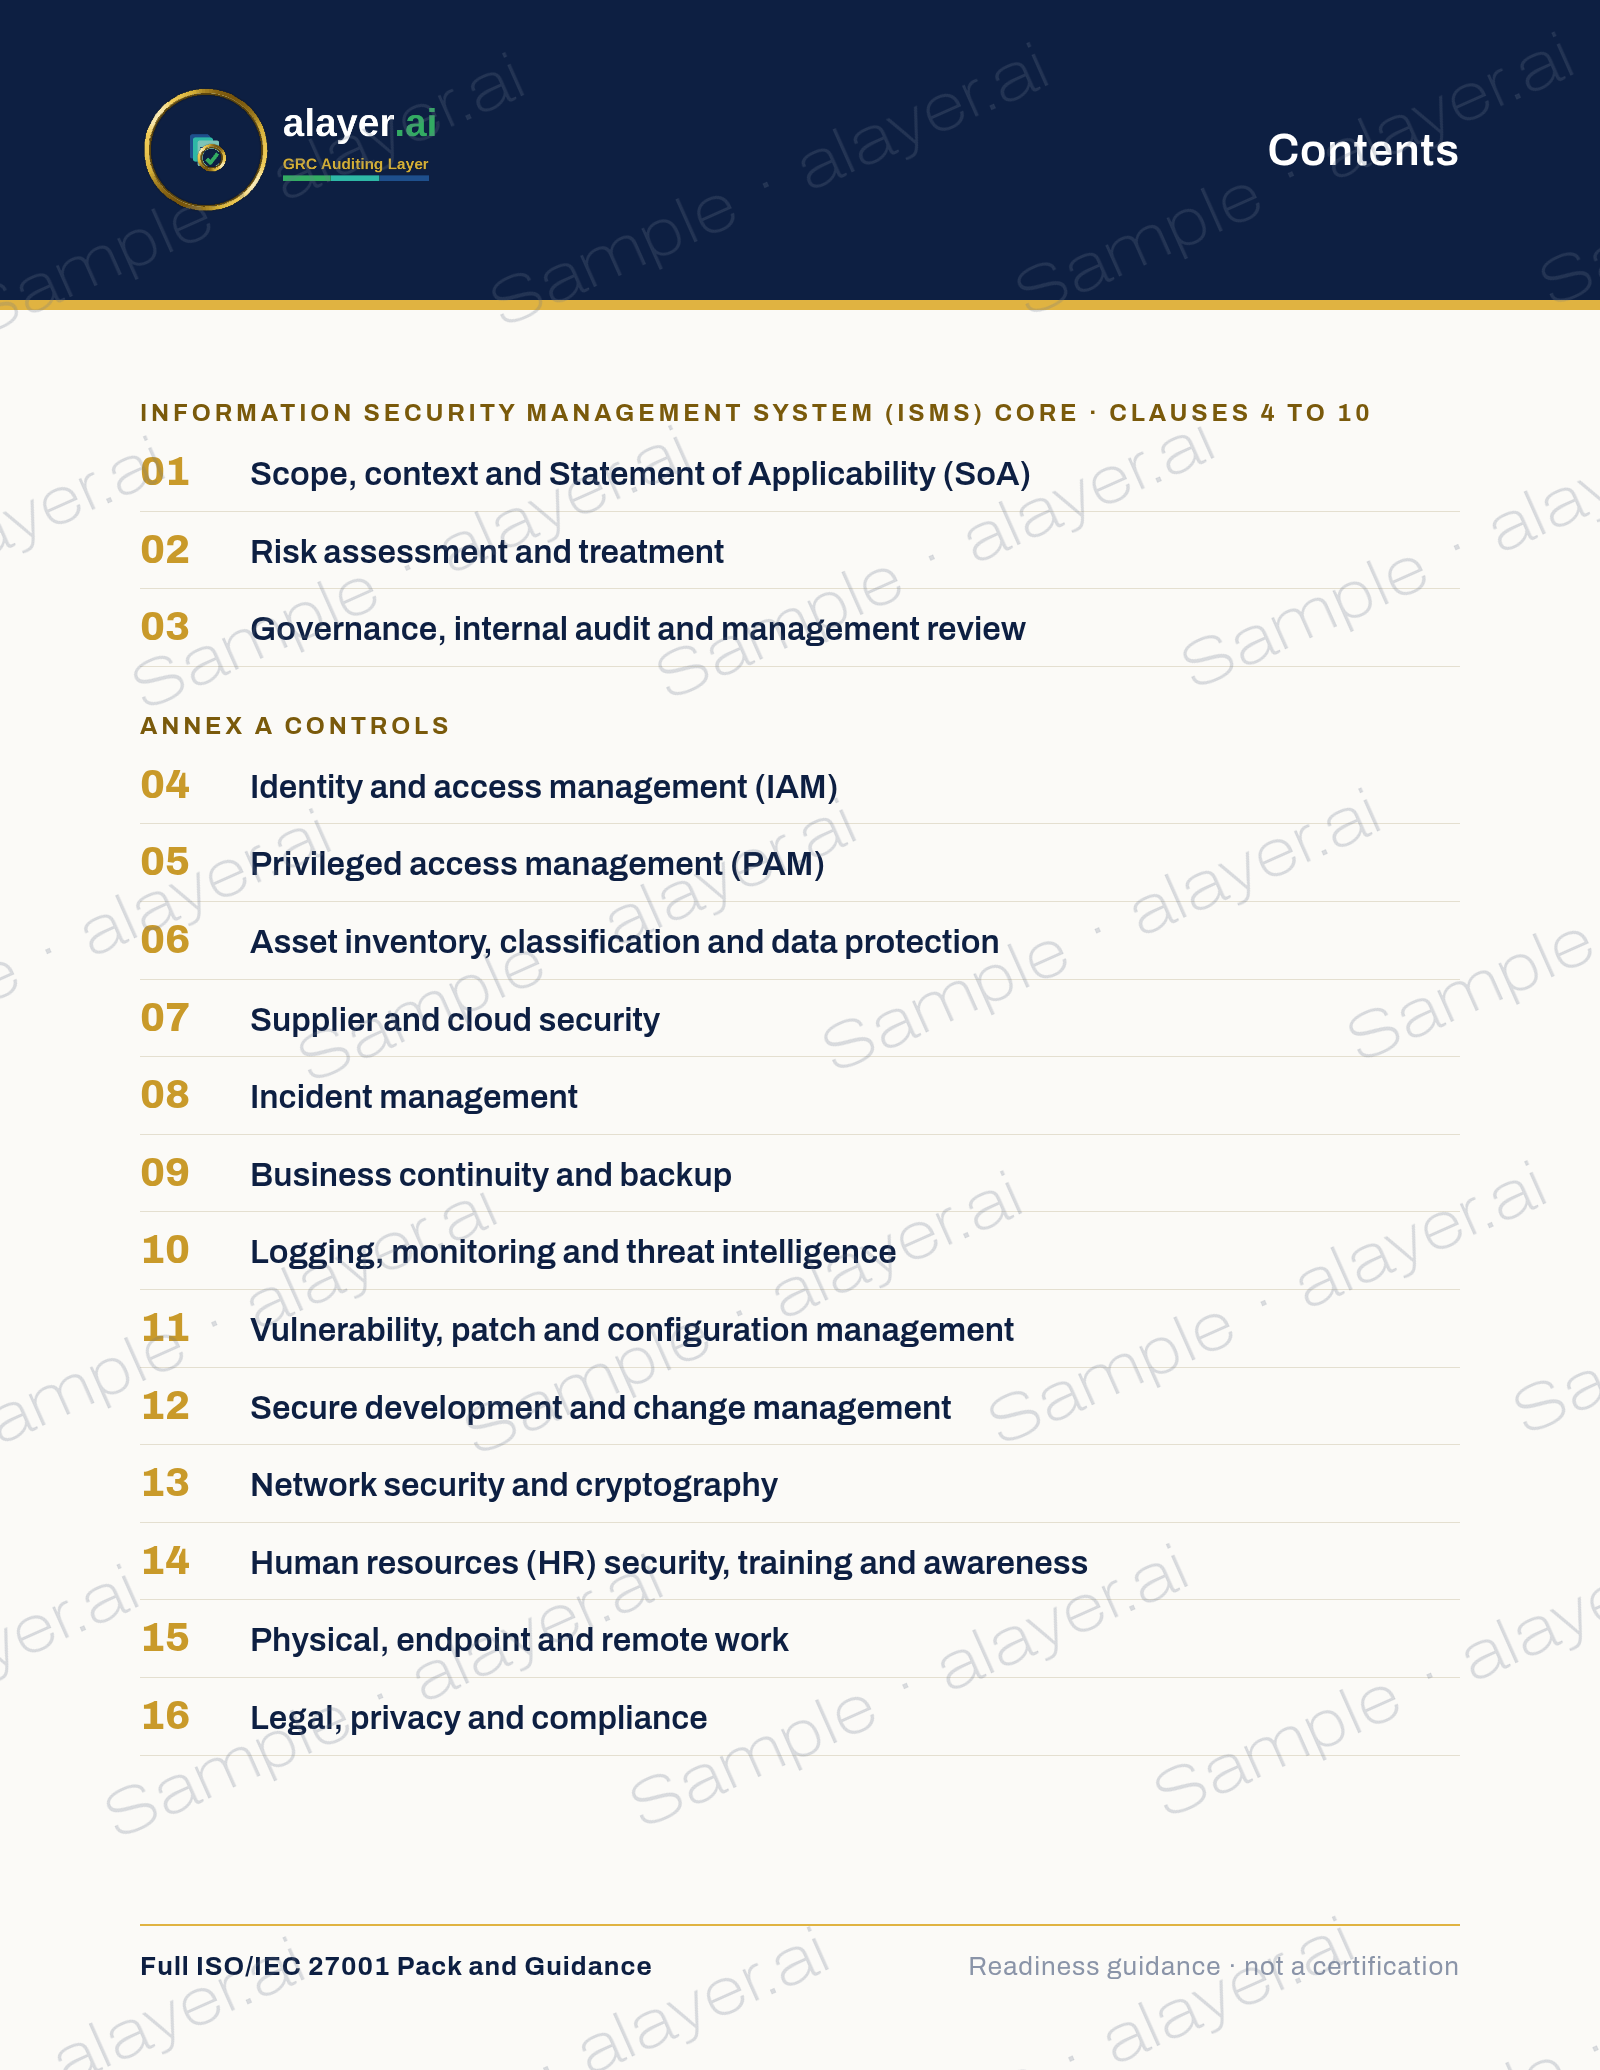
Preview pages from the pack: the table of contents and an illustrative Gap Assessment page.
What’s in the ISO 27001 documentation toolkit
An ISO 27001 documentation toolkit is a set of editable policies, registers and worksheets that your team adapts to its own scope and fills in with its own evidence. This toolkit has 25 Word, Excel and PDF files in 16 modules: the information security management system (ISMS) core for clauses 4 to 10, and the Annex A controls.
ISMS core · Clauses 4 to 10
- 01Scope, context and Statement of Applicability (SoA)
- 02Risk assessment and treatment
- 03Governance, internal audit and management review
Annex A controls
- 04Identity and access management (IAM)
- 05Privileged access management (PAM)
- 06Asset inventory, classification and data protection
- 07Supplier and cloud security
- 08Incident management
- 09Business continuity and backup
- 10Logging, monitoring and threat intelligence
- 11Vulnerability, patch and configuration management
- 12Secure development and change management
- 13Network security and cryptography
- 14Human resources (HR) security, training and awareness
- 15Physical, endpoint and remote work
- 16Legal, privacy and compliance
All 25 ISO 27001 templates and guides
See every document (25 files)
Start here
Pack Index and Role Map
Your starting point: which file goes to which team, and what to do first.
Used by: CISO and leadership
Module 1 · Scope, context and SoA
Gap Assessment
See where you stand today and where to start.
Used by: GRC
ISMS Scope Statement Template
Your ISMS scope statement, ready to fill in.
Used by: GRC
ISMS Registers
Your SoA worksheet and ISMS registers in one workbook, for your team to complete.
Used by: GRC
Module 2 · Risk assessment and treatment
Risk Register
Your risk register and treatment plan, ready to fill in.
Used by: GRC
Risk Methodology and Assessment Report
Your risk method and risk assessment report, written to be edited.
Used by: GRC
Module 3 · Governance, internal audit and management review
ISMS Policy Manual
Your information security policy set, written to be edited.
Used by: CISO and leadership
ISMS Governance Procedures
The procedures that keep your ISMS running, ready to adopt.
Used by: GRC
CISO Meeting Kit
Run the readiness project with meetings that end in decisions.
Used by: CISO and leadership
Module 4 · Identity and access management
IAM Evidence Guide for Microsoft Entra ID
Show your auditor the identity and access evidence they ask for.
Used by: Identity and access
Access Control Policy Template
Your access control policy, ready to fill in.
Used by: Identity and access
Joiner, Mover and Leaver Procedure
Grant, change and remove access cleanly as people join, move and leave.
Used by: Identity and access
Access Review Procedure
Run access reviews you can show your auditor.
Used by: Identity and access
Password and Authentication Standard
Your sign-in and password rules, ready to adopt.
Used by: Identity and access
Module 5 · Privileged access management
PAM Evidence Guide for Microsoft Azure and Microsoft Entra ID
Show your auditor how you control privileged and administrator access.
Used by: Cloud and platform engineering
Modules 6, 11 and 13 · Assets, vulnerabilities, networks and cryptography
IT Operations Evidence Guide
Show your auditor the evidence from your IT and infrastructure team.
Used by: IT and infrastructure operations
Module 7 · Supplier and cloud security
Supplier and Cloud Security Guide
Show how you choose, contract and review suppliers and cloud services.
Used by: Procurement and vendor management
Module 8 · Incident management
Incident Management Evidence Guide
Show your auditor how you handle incidents, start to finish.
Used by: Incident response
Module 9 · Business continuity and backup
Business Continuity and Disaster Recovery (DR) Evidence Guide
Show that you can keep running and recover when something breaks.
Used by: Business continuity and DR
Module 10 · Logging, monitoring and threat intelligence
Security Operations Evidence Guide
Show your auditor your logging and monitoring evidence.
Used by: Security operations
Module 12 · Secure development and change management
Secure Development Evidence Guide
Show that security is built into how you build and change software.
Used by: Software engineering
Module 14 · HR security, training and awareness
HR Security Guide
Your HR team’s part of ISO 27001 readiness, in plain language.
Used by: HR
Module 15 · Physical, endpoint and remote work
Facilities and Physical Security Guide
Your facilities team’s part of ISO 27001 readiness, in plain language.
Used by: Facilities
Module 16 · Legal, privacy and compliance
Legal and Compliance Guide
Keep your legal and regulatory commitments on record for your audit.
Used by: Legal
Privacy Guide
Your privacy team’s records and requests, ready for your audit.
Used by: Privacy
16 modules. 25 editable files.
Word, Excel and PDF.
One file per area of work
Hand each one to whoever owns it. Small team? One person can own several areas. First task, for example: “Trace one leaver end to end.”
Gap Assessment
Decide which ISO/IEC 27001:2022 Annex A controls apply to your risks and scope, record those choices, and see which of the 16 modules need the most work.
Identity and PAM evidence guides
Identity and access management (IAM), 40 pages, and privileged access management (PAM), 79 pages, for engineers who work with Microsoft Entra ID and Microsoft Azure: the evidence an auditor asks for, and how to produce it.
CISO Meeting Kit
“The goal is decisions, not a presentation.” Everything you need to run the readiness project from kickoff to your Stage 1 audit.
Registers and SoA worksheet
ISMS Registers workbook, with an SoA worksheet your team completes, plus a Risk Register.
Policies and procedures
An ISMS Policy Manual and governance procedures, including internal audit and management review, written to be edited.
In a 2026 Huntress survey of 504 U.S. IT and security managers, 37% said compliance and audit demands led to security team burnout or staff turnover in the past year.
Source: Huntress, huntress.com/blog/audit-readiness-gap (published August 2026).
Full ISO/IEC 27001 Pack
25 editable files in 16 modules. One download.
Single Registered End-User license, under the End User License Agreement (EULA) and the refund policy.
ISO 27001 toolkit FAQ
How does the license work?
One purchase licenses one named person. Your name and a unique license number are stamped on the files. Your organization may keep the filled-in documents you make from them and share those with its auditors. You may not share the original pack across your organization, resell it or publish it. Full terms are in the EULA.
Will this get us certified?
No, this pack will not get you certified: it is readiness guidance, not a certification. It is not legal advice, and Alayer.AI does not supply or sign your SoA.
Who is it for?
It is for the CISO running ISO/IEC 27001:2022 readiness, and for the people who supply the evidence. The GRC lead uses the Gap Assessment, registers and risk files. Identity and cloud engineers use the evidence guides for Microsoft Entra ID and Microsoft Azure. Each other area of work has its own guide.